What Is an OT Cyber Security Audit, Monitor and Review Process?
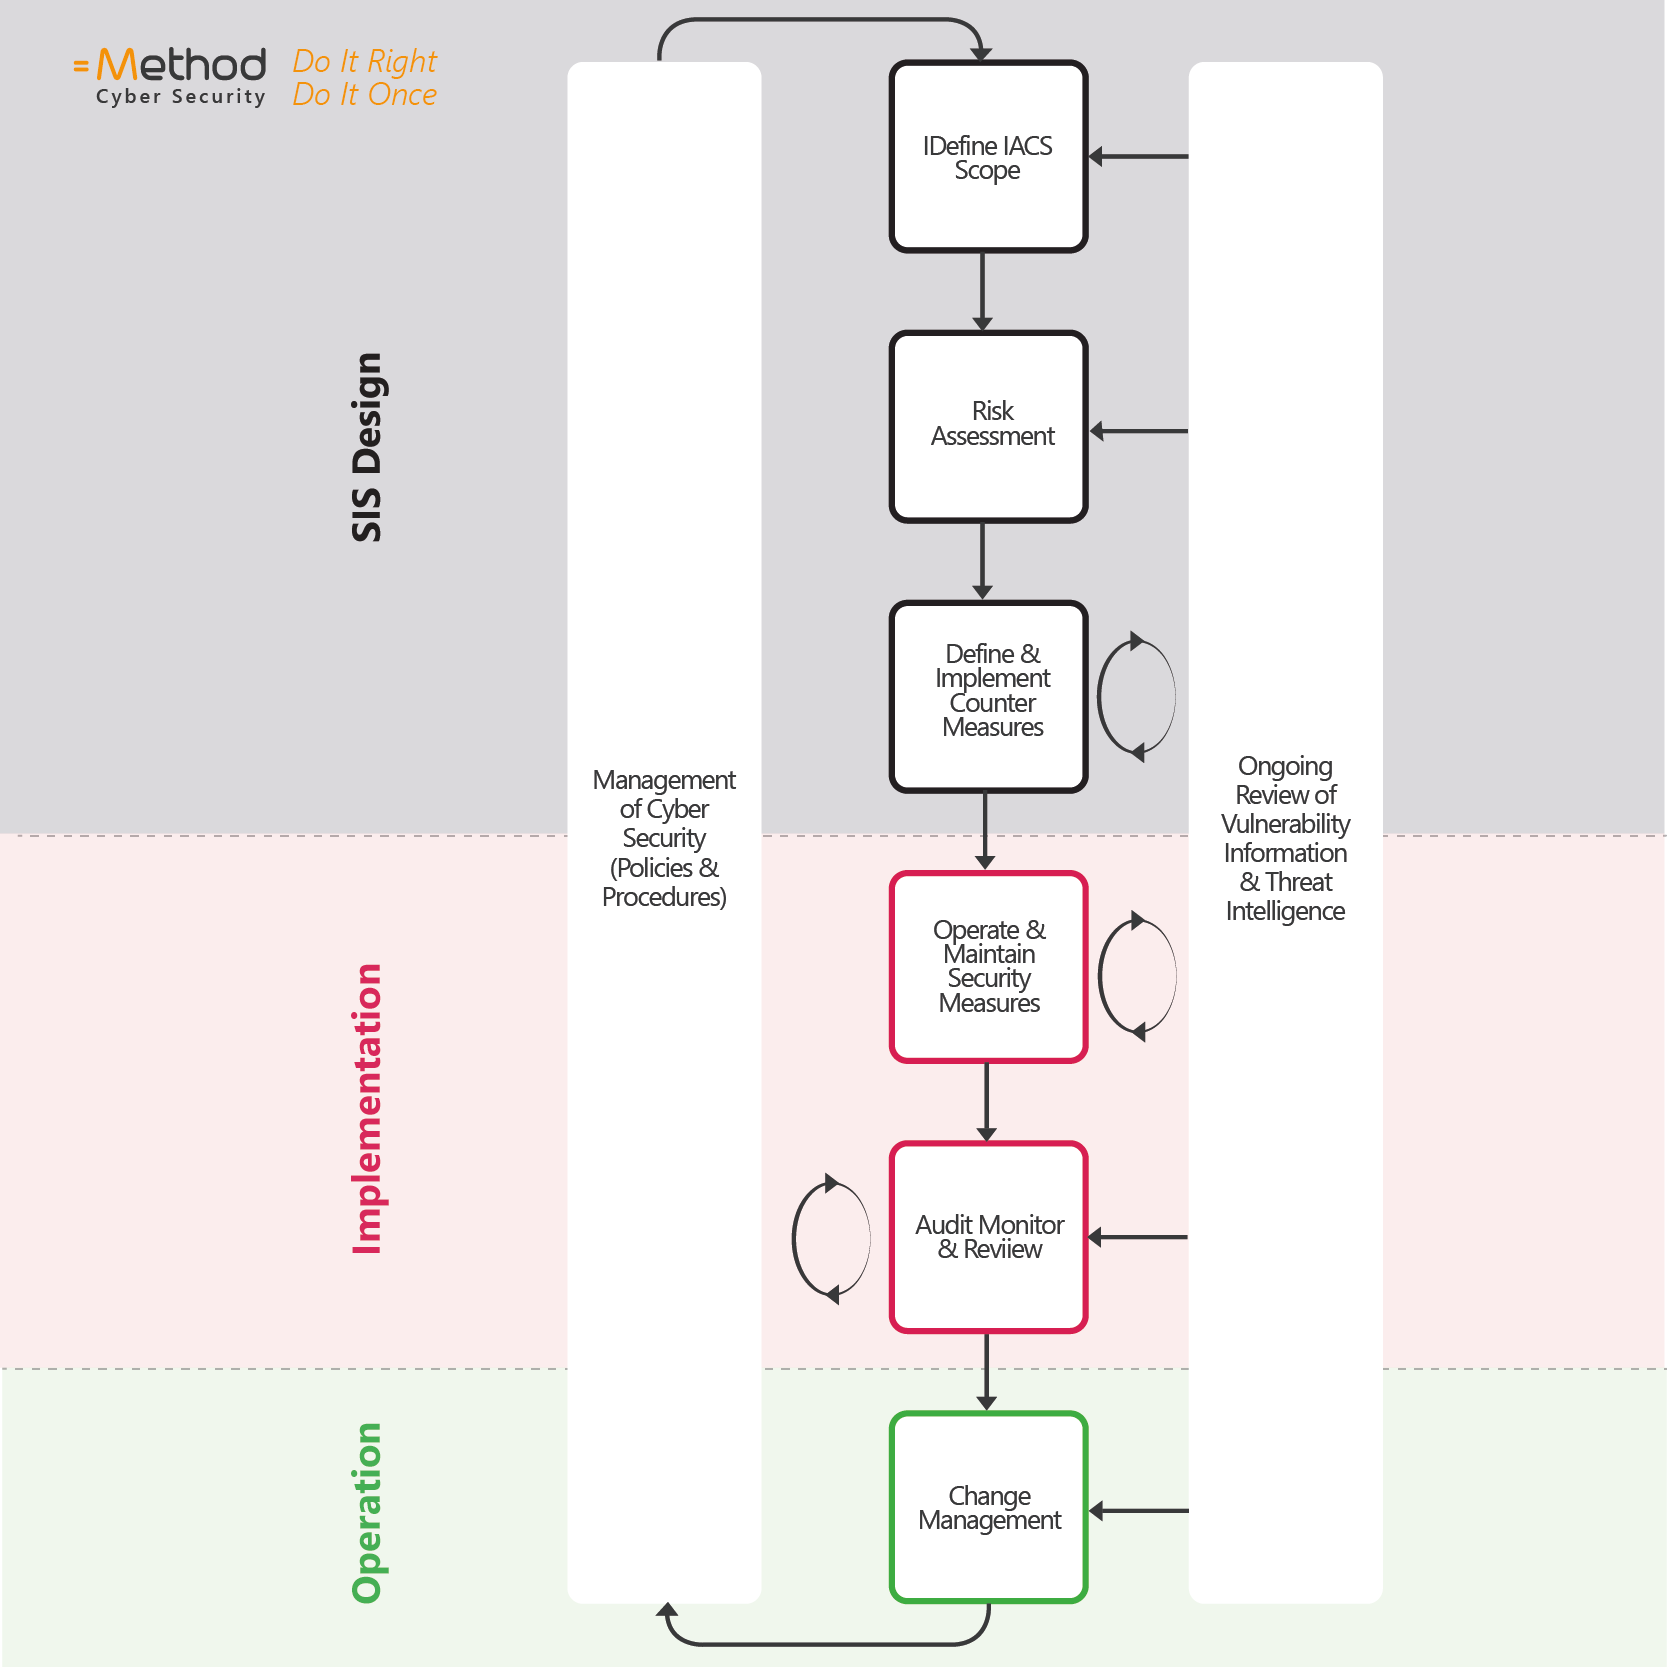
The Cyber Security Management System (CSMS) audit, monitoring and review process will provide evidence of compliance with the CSMS policies and procedures and allow re-evaluation of the assumptions underpinning the policy and procedures by reviewing the organisational security posture on the basis of an on-going awareness of current vulnerability information and threat intelligence.
Regular auditing, both by internal self-assessment and formal third-party audits, will drive continuous improvement of an organisation’s CSMS and can be controlled as part of the CSMS itself or incorporated, as a means of highlighting cyber security concerns, into the overall site or organisation management system, although the frequency of cyber security audits should take into account the constantly changing threat landscape. The findings of audits, monitoring and review exercises will be used to highlight any areas for improvement in an organisation’s CSMS or security posture and should be reported at board level to secure funding to mitigate critical concerns.
The audit, monitoring and review process will also help to identify any undocumented additions, suspensions or changes to your organisation’s simple network diagram and IACSIndustrial Automation and Control Systems asset register which should have been captured by the Change Management process.
Technical author
Steve Essery
Technical Director at Method Cyber Security & Group Quality Assurance Manager at Method Safety and Security
Since 2019, Steve has worked as a contract Functional Safety Professional and Cyber Security Specialist, and as a Regulatory Compliance Consultant and Equipment & Control Systems Validation Specialist within the pharmaceutical industry, before becoming a Technical Director at =Method.