What is a Cyber Security Management System (CSMS)?
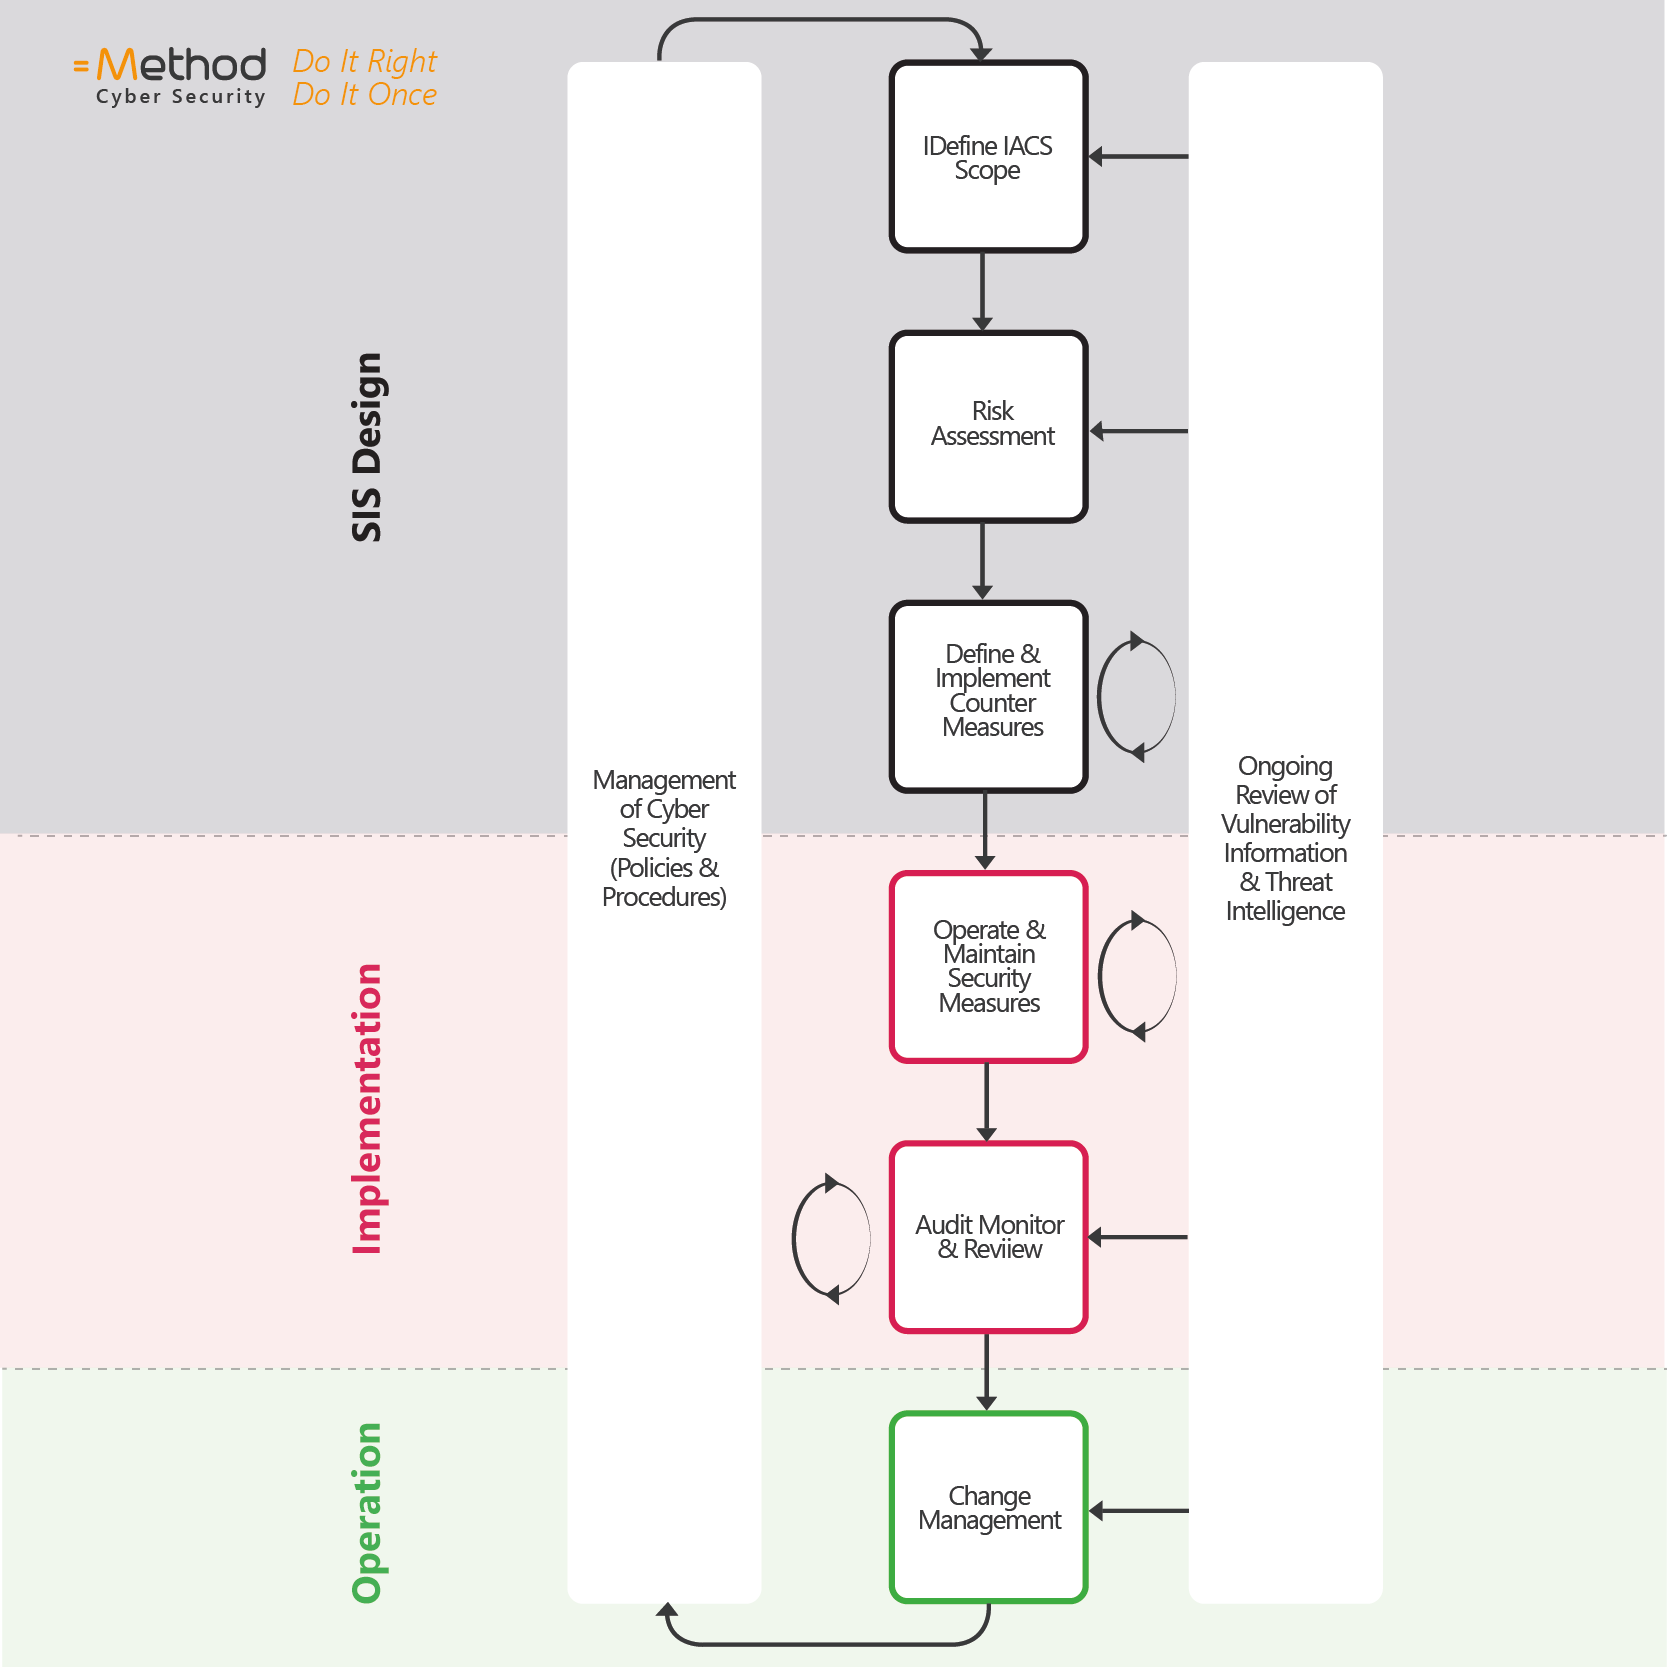
The management of cyber security risk requires to be an ongoing iterative process, which reacts to a constantly evolving threat landscape, driven by the organisation’s understanding of their vulnerabilities and informed by an awareness of adversaries’ methods.
A Cyber security Management System (CSMS) should be developed, adopted by senior management, and incorporated into the organisation’s existing policies and management systems. The structure of the CSMS can follow existing management systems e.g. those outlined in specific security standards such as IEC 62443ISA TR84.00.09, or ISO 27001, as specified in the functional safety for the process industry sector IEC 61511, or other regulatory framework specific to the organisation.
Any CSMS should contain policies and procedures to address the following objectives and cyber security principles (excerpt from NCSC CAF)
- A. Managing security risk
- 1 Governance
- 2 Risk management
- 3 Asset management
- 4 Supply chain
- B. Protecting against cyber attack
- 1 Protection policies and processes
- 2 Identity and access control
- 3 Data security
- 4 System security
- 5 Resilient networks and systems
- 6 Staff awareness and training
- C. Detecting cyber security events
- 1 Security monitoring
- 2 Proactive security event discovery
- D. Minimising the impact of cyber security incidents
- 1 Response and recovery planning
- 2 Lessons learned
The policy, procedures and management system documents produced will require to be adopted and championed at board level and trained out to all personal with the potential to interact with or impact the security of IACS assets. This effectively requires all personnel within an organisation to have a basic level awareness or enhanced, role-specific training in OT cyber security.
The CSMS documents will require to be frequently reviewed and updated, as necessary, in light of evolving threats and newly discovered vulnerabilities, in line with the concept of continuous improvement.
Appendix 2 of OG86 suggests suitable document types that organisations can present as evidence of each aspect of their CSMS.
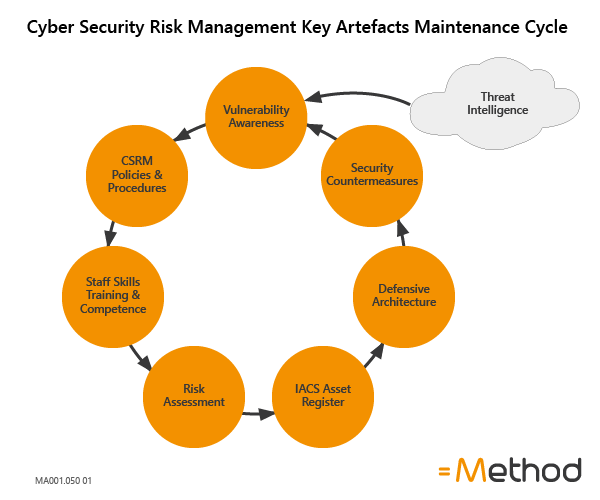
Diagram 1. Cyber Security Risk Management Key Artefacts Maintenance Cycle
Technical author
Steve Essery
Technical Director at Method Cyber Security & Group Quality Assurance Manager at Method Safety and Security
Since 2019, Steve has worked as a contract Functional Safety Professional and Cyber Security Specialist, and as a Regulatory Compliance Consultant and Equipment & Control Systems Validation Specialist within the pharmaceutical industry, before becoming a Technical Director at =Method.